Tap your card. Transaction complete. No PIN. No signature. No friction. That's the whole point of Near Field Communication - payments fast enough that you barely notice them. Fraudsters have noticed, though. And they've been busy.
NFC technology powers tap-to-pay contactless cards, mobile wallets (Apple Pay, Google Pay, Samsung Pay), and transit systems worldwide. With contactless payments now representing the majority of in-person transactions in many countries, NFC has moved from novelty to critical financial infrastructure - and from obscure technology to active fraud target.
How fraudsters exploit NFC technology:
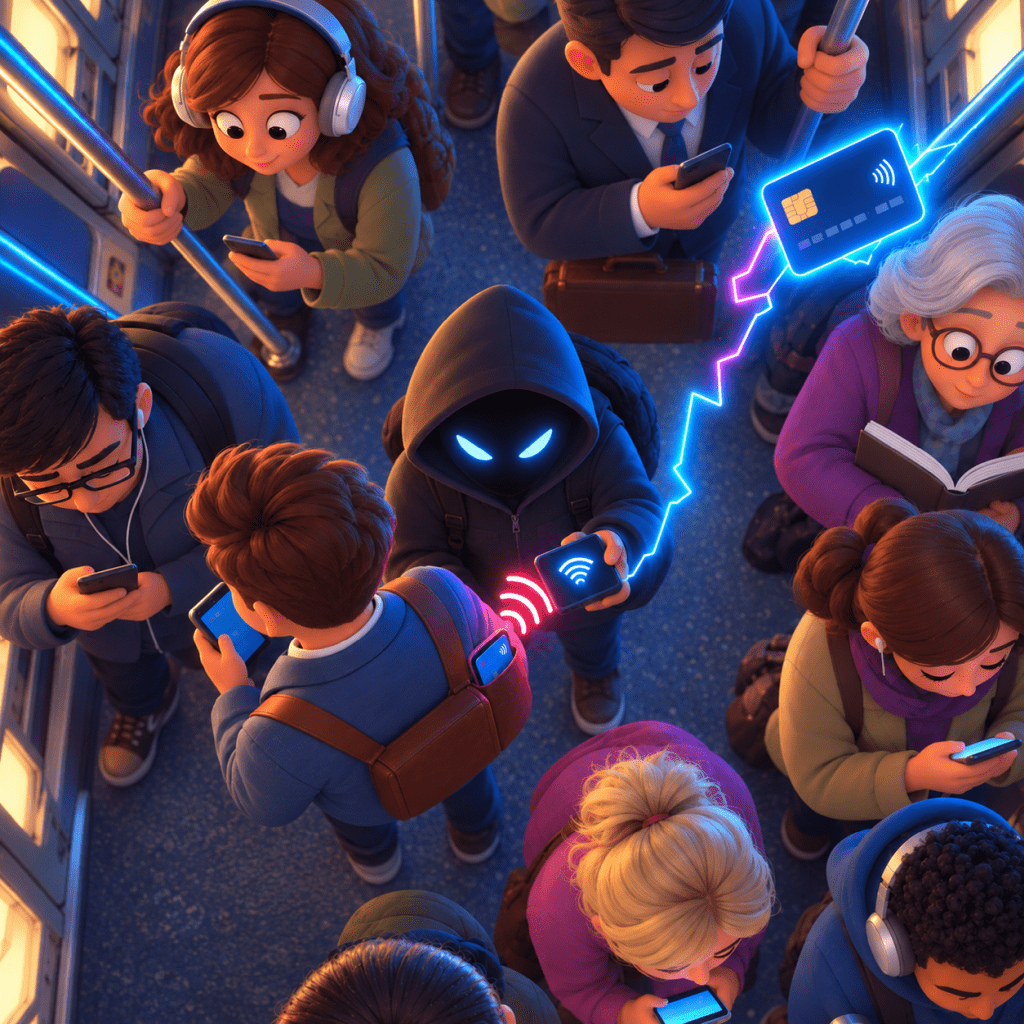
📡 Proximity reading and skimming - NFC operates at a typical range of 4-10cm, but specialized hardware can read NFC cards at distances of up to 50-90cm. Researchers have demonstrated the ability to read contactless card data - card number, expiry, and in some cases the cardholder name - from a crowded subway or elevator, without the cardholder's knowledge. This data can be used to create virtual cards for online fraud.
💳 Relay attacks - A two-device attack where one device placed near the victim's card captures the NFC signal and relays it in real time to a second device near a payment terminal. The terminal sees a genuine card response. The victim's card has been "teleported" to a fraudulent transaction. Relay attack toolkits have been demonstrated at security conferences and are available to motivated criminals.
📱 Malicious NFC tags and "quishing" - NFC tags embedded in posters, restaurant menus, parking meters, or QR-code alternatives can be manipulated to direct victims to phishing pages when scanned with a smartphone. A fraudulent NFC tag placed over a legitimate one (in a hotel room, at a charging station, or on a public notice) redirects the victim's phone to a malicious site for credential harvesting.
🔓 Stolen device exploitation - Apple Pay, Google Pay, and similar mobile wallets often require biometric authentication for payment. But some older implementations, transit modes, and express payment settings allow payments without authentication. A stolen phone can enable contactless payments before remote wipe is completed - particularly on transit systems with simplified authentication.
🏪 Merchant-side NFC manipulation - Compromised or malicious point-of-sale terminals can capture NFC card data for later fraudulent use, or manipulate transaction amounts between the tap and the authorization. Unlike magnetic stripe cloning, NFC tokenization limits but does not eliminate this risk.
🌐 Digital pickpocketing - The practical threat of remote NFC reading in crowded spaces - trains, airports, shopping queues - is well-documented by researchers. While most real-world exploitation uses other methods (contactless fraud losses are relatively small compared to digital channels), the attack vector is real and consumer awareness remains low.
In practice, contactless payment fraud represents a relatively small share of total card fraud - partly because NFC tokenization means the card number transmitted is a one-time token, not the actual PAN. However, relay attacks and NFC tag manipulation represent growing threat surfaces as NFC adoption extends beyond payments into door access, healthcare, and identity documents.
What can we do:
For individuals:
- Use RFID/NFC-blocking card sleeves or wallets for contactless cards if you have concerns about proximity reading in crowded environments.
- Enable payment notifications on your bank app for all contactless transactions - you'll know immediately if your card is used without your knowledge.
- Set contactless payment limits and require PIN for transactions above your comfort threshold.
- Be cautious about scanning NFC tags from unfamiliar sources - treat them with the same skepticism you'd apply to unknown QR codes.
For organizations:
- Regularly inspect payment terminals and NFC-enabled access points for tampering - card skimming devices and fraudulent NFC tag overlays are designed to look legitimate.
- Implement transaction monitoring that flags unusual contactless payment patterns.
- For authentication in high-risk contexts (building access, healthcare records), do not rely on NFC alone - implement additional authentication factors.
Tap carefully. Not all readers are reading what you think they're reading.